On-demand application pentests
Obtain a scoped test and compliance-ready report without a lengthy manual scheduling cycle.
Independent tool overview
XBOW is an autonomous offensive-security platform that maps web applications and APIs, attempts scoped attacks, validates exploitable vulnerabilities, and returns reproducible evidence and remediation guidance.
Visit the official XBOW site ↗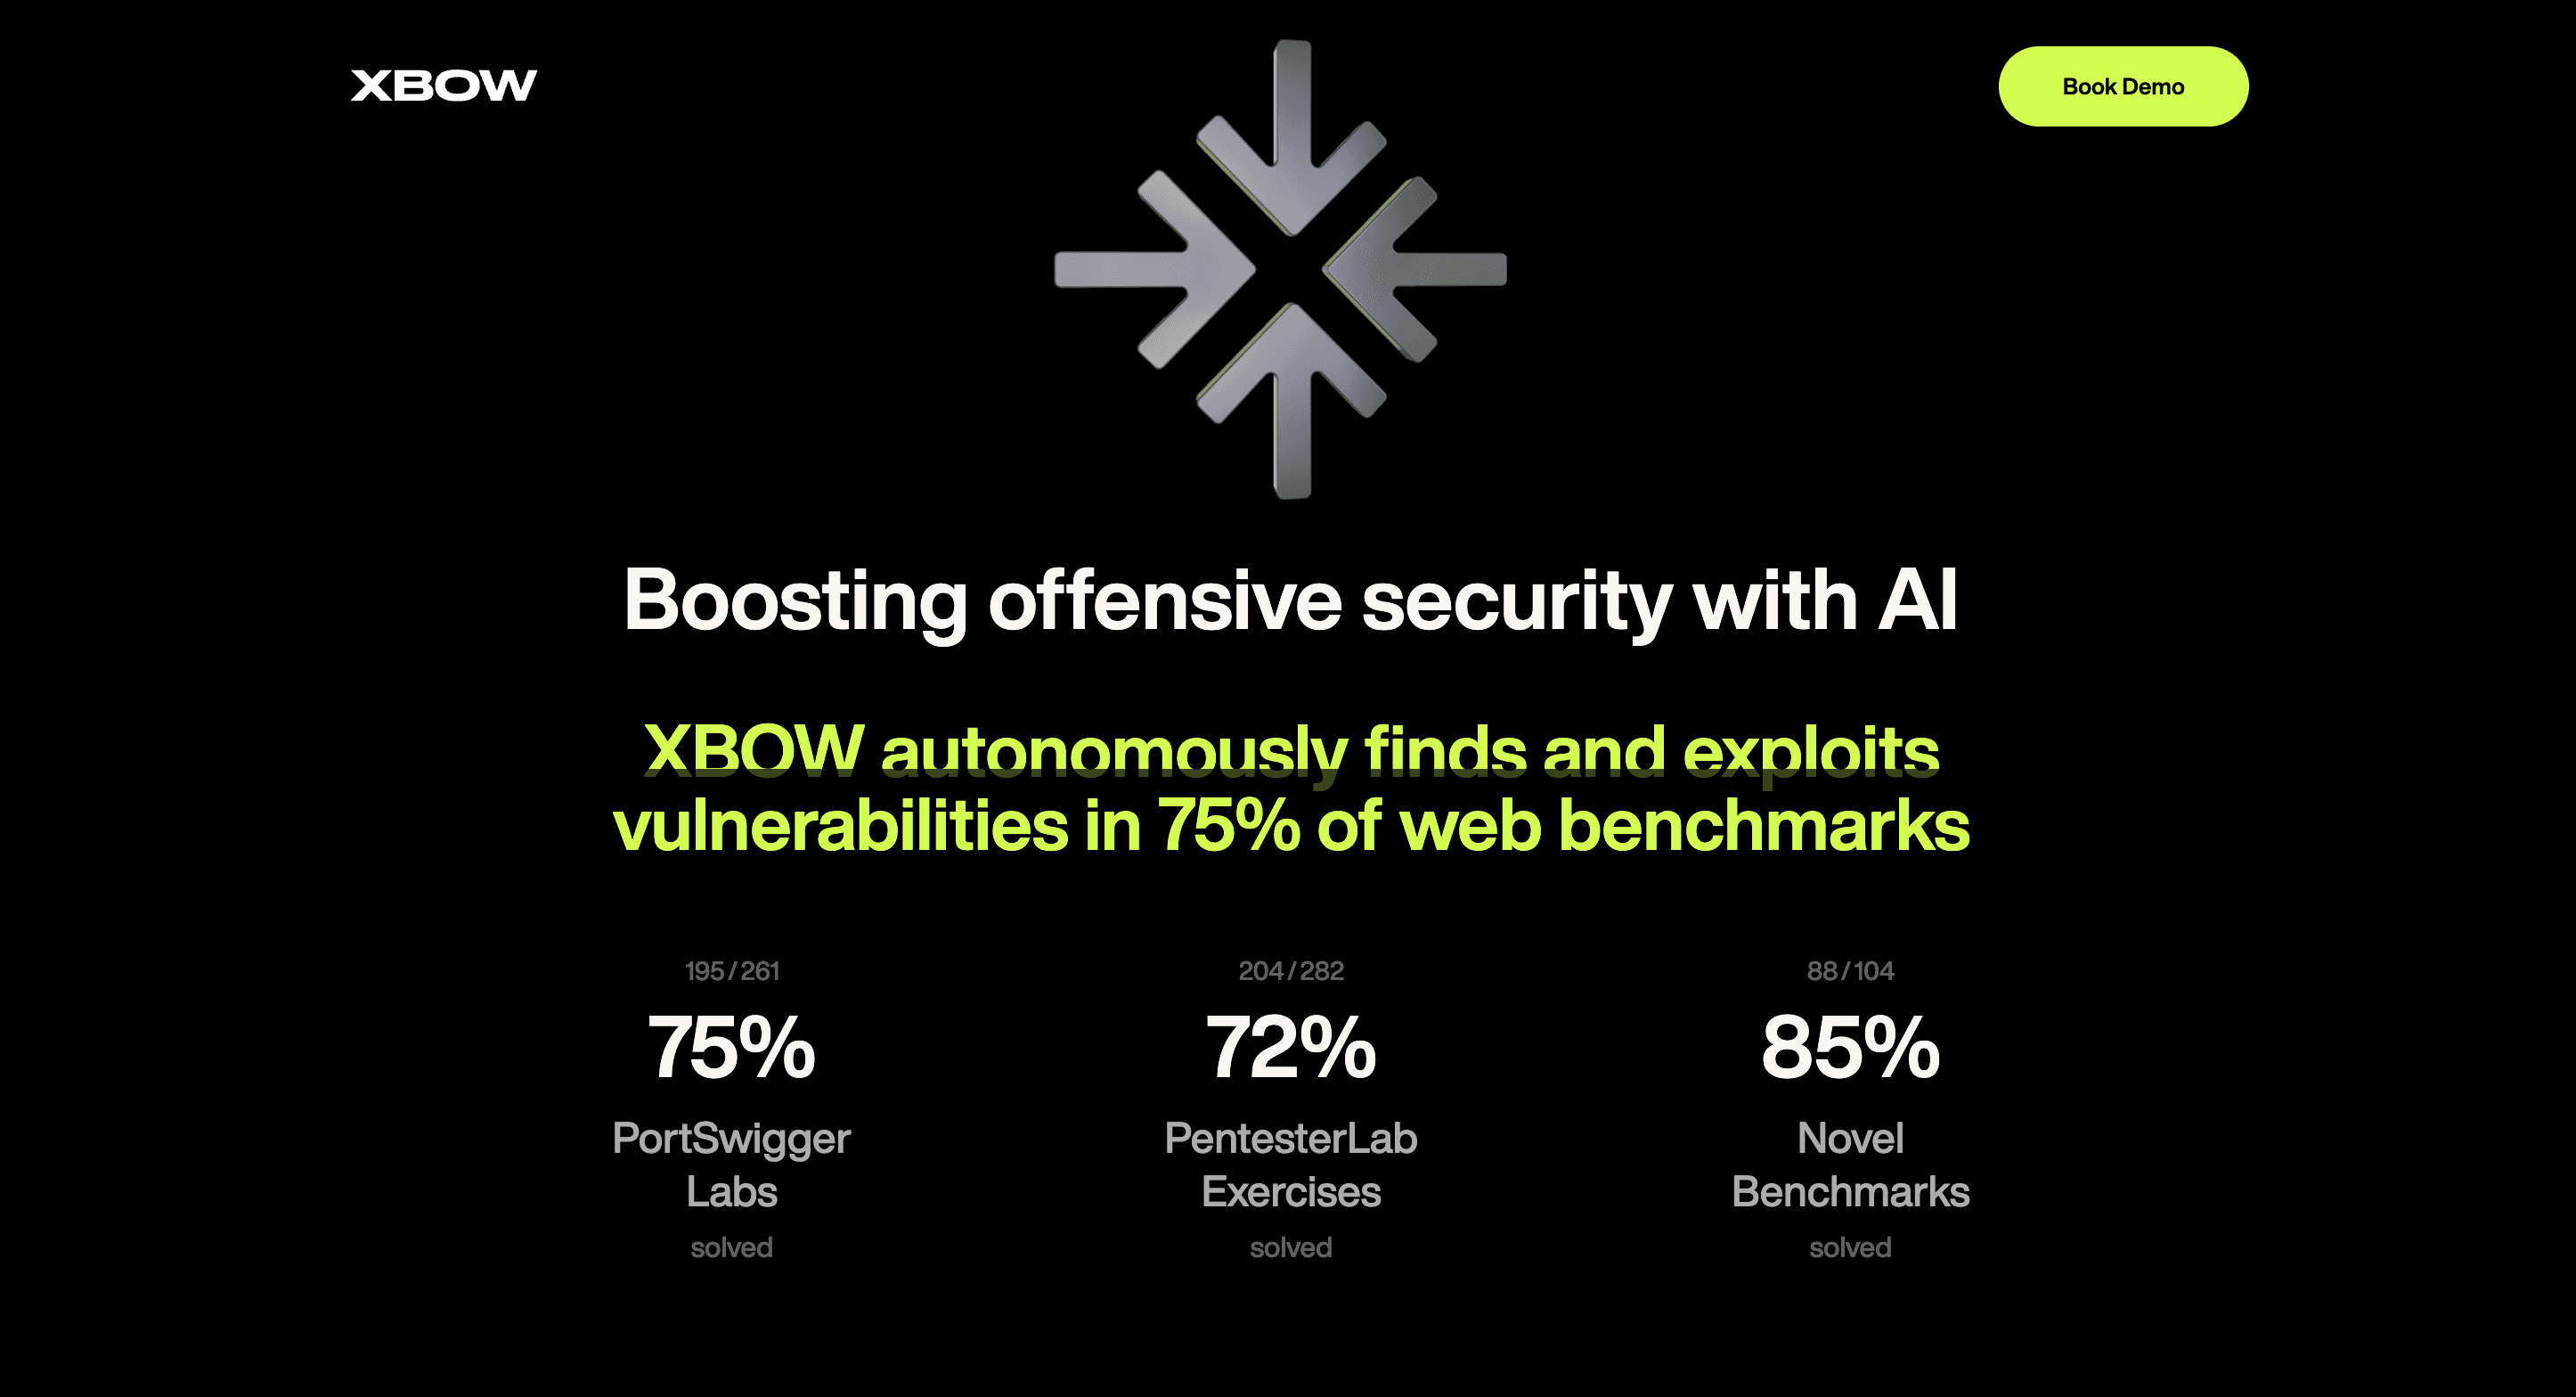
Overview
XBOW uses coordinated AI agents and offensive-security tools to conduct penetration tests against web applications and APIs. After a team defines an authorized target and supplies useful context such as credentials, API specifications, and architecture notes, the platform maps the attack surface, explores possible paths, and attempts to prove which weaknesses are genuinely exploitable.
The product emphasizes validated findings rather than speculative alerts: independent validators confirm exploits, and teams can inspect the attack path and supporting evidence. XBOW offers on-demand engagements for point-in-time needs and an enterprise platform for continuous portfolio coverage, APIs, governance, and integrations.
Use cases
The strongest fit depends on the job you need the product to complete, not the size of its feature list.
Obtain a scoped test and compliance-ready report without a lengthy manual scheduling cycle.
Retest frequently as applications and APIs change instead of relying on a single annual snapshot.
Coordinate testing and validated findings across many internet-facing assets through one platform and API.
Capabilities
Builds a live view of pages, endpoints, parameters, authentication flows, and possible attack paths.
Directs focused workers to explore and chain vulnerabilities in parallel.
Uses independent validators and working proofs to confirm exploitability before surfacing a finding.
Shows the attack path, evidence, decision log, mitigation guidance, and information needed to reproduce the issue.
Runs targeted checks against remediated vulnerabilities to confirm that fixes hold.
Supports programmatic assessments plus enterprise workflows with Microsoft Sentinel and Security Copilot.
Process
Step 1
Identify assets the organization owns or is explicitly permitted to test, then define boundaries and safety requirements.
Step 2
Add URLs, credentials, API specifications, architecture notes, and other information that can deepen coverage.
Step 3
XBOW maps the application, coordinates attack agents, and validates potential exploits within the approved scope.
Step 4
Review evidence and mitigation guidance, fix confirmed issues, and run focused retests before closing findings.
Cost
XBOW Pentest On-Demand starts at $4,000. Enterprise pricing is usage based and scoped to the customer's environment, coverage, and portfolio. XBOW is also sold through AWS, Google, Oracle, and Microsoft cloud marketplaces.
From $4,000
A self-service, point-in-time autonomous penetration test with results targeted within five business days.
Custom usage-based quote
Continuous offensive-security coverage sized to the environment and application portfolio.
Pricing checked . Check current pricing at the source ↗
Assessment
Compare
The right alternative depends on the specific output, workflow, controls and budget your project requires.
Coding
Choose Claude Security when the primary need is repository-level vulnerability analysis and proposed code fixes.
Explore Claude Security →Agents
Choose Codex Security for agentic source-code scanning, validation, and patching workflows.
Explore Codex Security →Coding
Choose Dryrun Security for developer-focused code security context inside the pull-request workflow.
Explore DryRun Security →Questions
XBOW is designed to assess web applications and APIs, including common flaws such as injection, cross-site scripting, server-side request forgery, exposed credentials, misconfigurations, and chained attack paths.
It automates substantial application pentesting and includes validated evidence, but organizations may still need human-led work for specialized business logic, broader threat scenarios, governance, and compliance requirements. XBOW says marketplace engagements include final human expert review.
XBOW says Pentest On-Demand starts at $4,000. Continuous enterprise pricing is usage based and requires a quote scoped to the environment.
Yes. Retests focus on the relevant attack types or checks to verify whether a reported issue has been fully remediated.
XBOW documents scope controls, non-destructive validation, audit trails, and configurable safeguards, but each organization remains responsible for authorization, boundaries, credentials, monitoring, and change-management controls.
Bottom line
XBOW is a compelling option for security teams that want faster, repeatable application pentesting with evidence that findings are exploitable. Its strongest value is continuous validation across changing applications, but it should sit inside a mature, explicitly authorized security program rather than be treated as a replacement for all human testing and risk management.
Visit XBOW website ↗
Get access to all our AI courses, hundreds of real-world AI use cases, live expert-led workshops, an exclusive network of AI early adopters, and more.
Get unlimited access to all of our current & upcoming industry-specific AI courses for the duration of your subscription.
To keep up with the rapid pace of AI, our team publishes AI implementation guides daily. Our library contains 300+ practical use cases to automate real-world work.
Join weekly, live, interactive sessions with industry leaders who are at the forefront of AI for hands-on implementation guidance and exclusive insights.
Network with an exclusive community of AI-first professionals who are working smarter with AI. Learn how early adopters are using AI in their work and businesses.


